KeeneticOS 5.2
KeeneticOS release notes for Keenetic Sprinter (KN-3711) in the Preview Channel
KeeneticOS releases in this channel provide the chance to be among the first to try the latest updates, performance improvements and new features, all with minimal risk. It is updated roughly every two weeks, with major updates about every two months. Releases here are typically more than a month in advance of release to the general audience in the Main Channel.
Keenetic Sprinter (KN-3711) is currently in the Standard Updates support period and receives regular software updates, including security enhancements, new features, operating system updates, and bug fixes.
KeeneticOS 5.2 Beta 1
19/10/2026
New
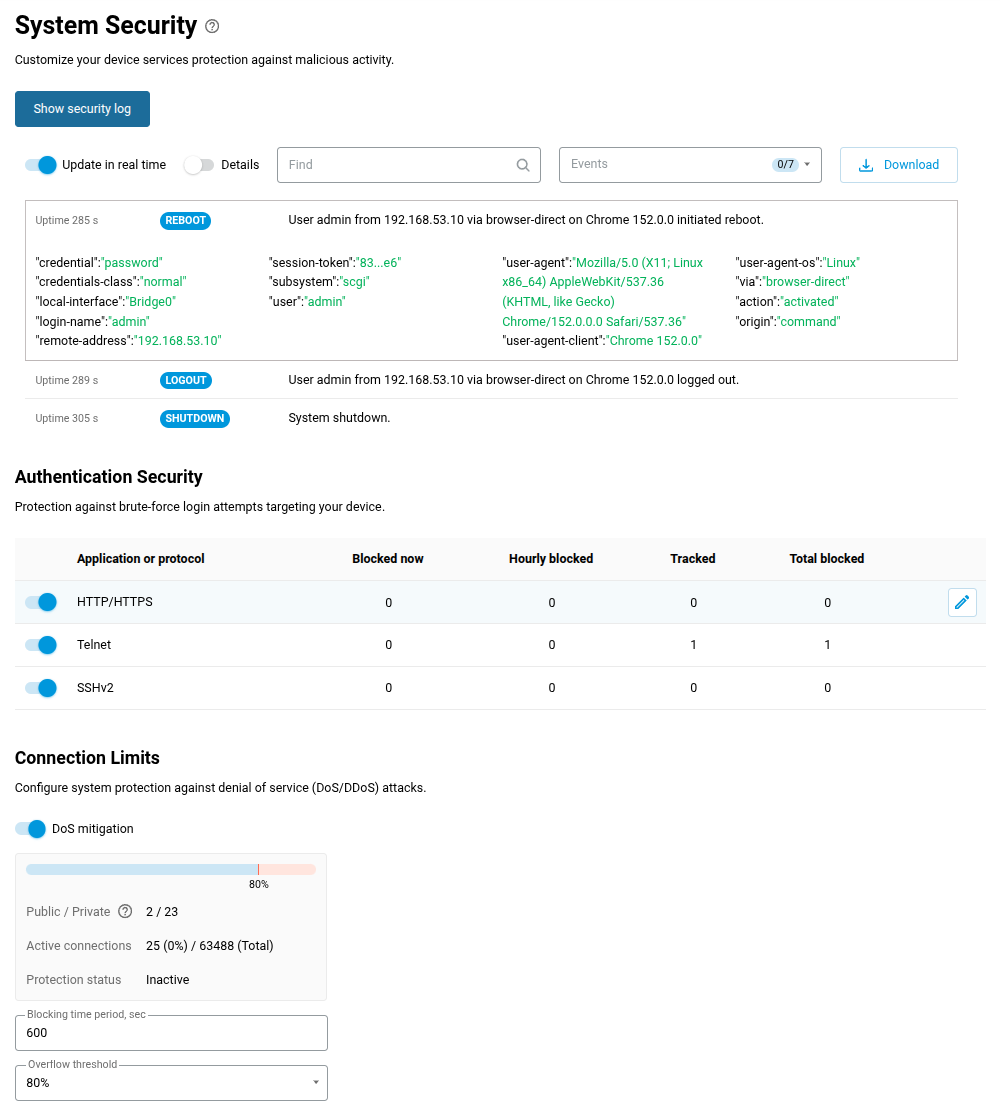
Added System Security page featuring a display of system events in the Security Log, brute-force protection settings for network services, and DoS attack mitigation controls. [NWI-5104]
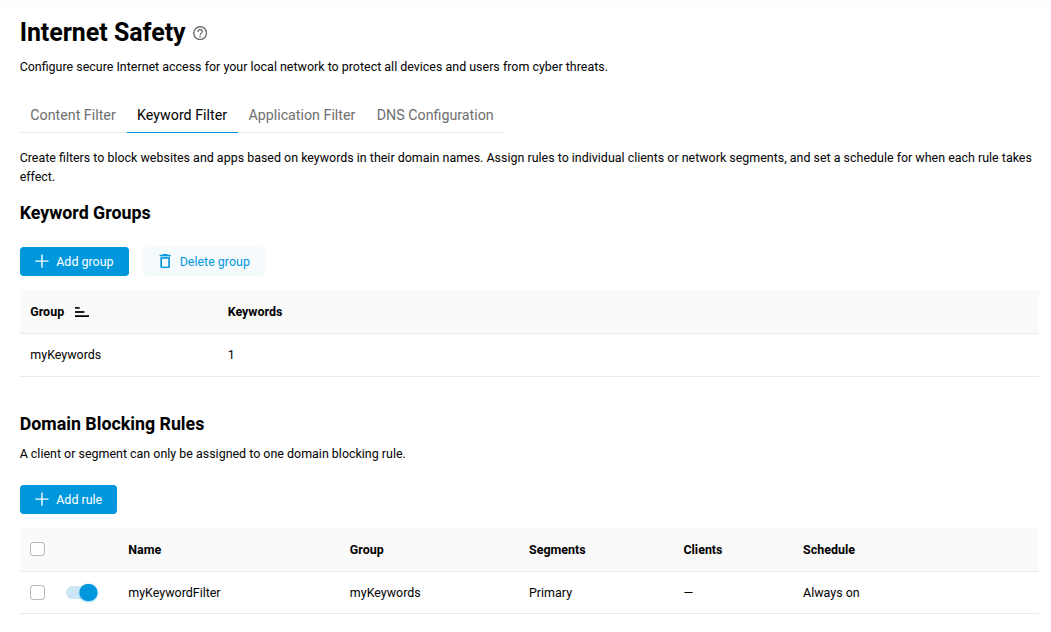
Added a Keyword Filter tab to the Internet Safety page to enable domain name blocking based on keyword groups. [NWI-4963]
Implemented a command to manage and assign keyword filtering profiles for domain names, available with the installation of the Domain keyword filtering system component. [NDM-4285]
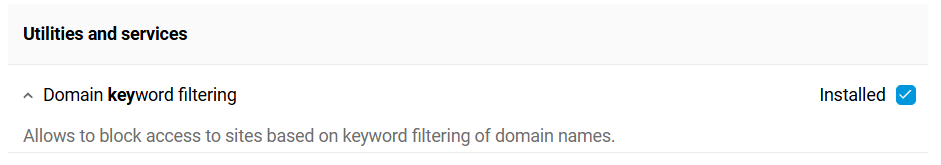
ip hotspot filter (profile {name} [description {description}] [object-group {group}] [schedule {schedule}] [enable]) | (assign (interface {interface} | host {mac}) {profile})— create and manage, or assign the keyword profile to filter domain names in network traffic.
Introduced a new CLI command to assign FQDN-based routes to custom connection policies. [NDM-4423]
ip policy {name} dns-proxy route object-group {group} (({gateway} [{interface}]) | ({gateway} [{interface}]) | {interface}) [auto] [reject] | rule— add an FQDN-based route to{name}connection policy.
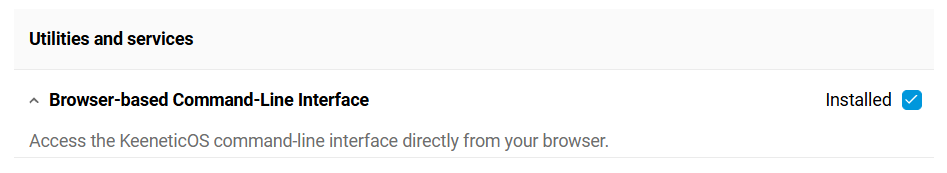
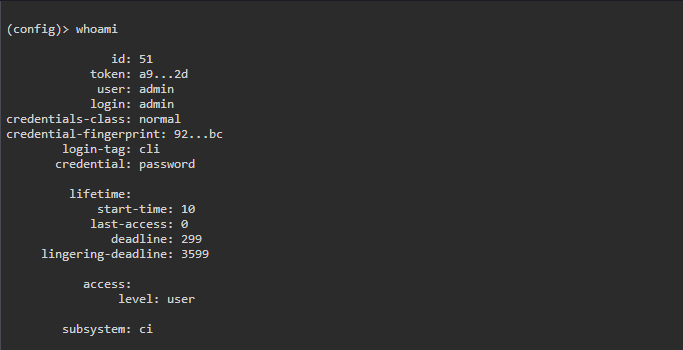
Implemented the web-based command line system shell, accessible from the right slide-out menu after installing the Browser-based Command-Line Interface system component. [NWI-4900]
Improved
The following improvements have been applied to the Web Interface.
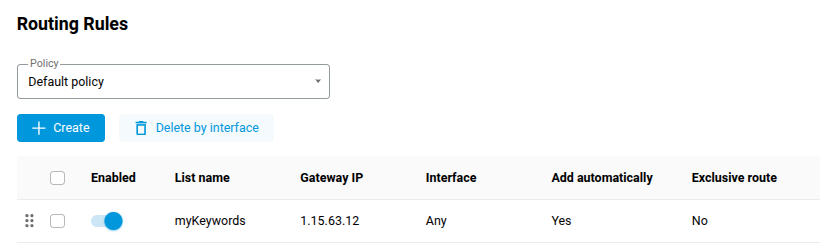
Added a Policy selector to the Routing menu, enabling configuration of separate routing tables for each Internet access policy. [NWI-5088]
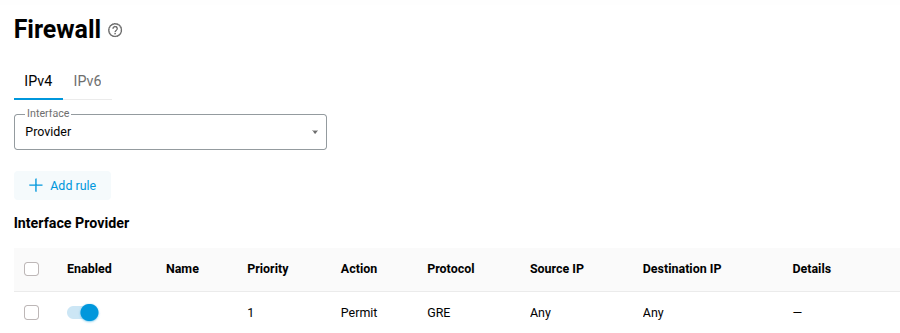
Added an Interface selector to the Firewall menu for quick access to rules for a specific network. [NWI-5089]
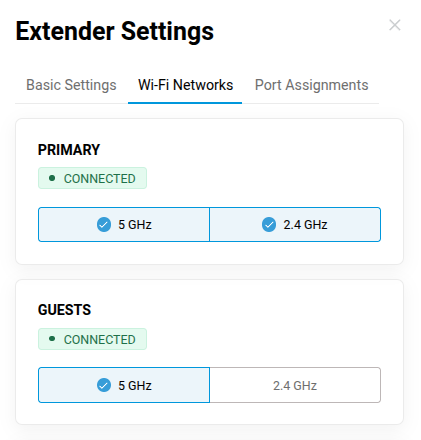
Added the Wi-Fi Networks tab to Extender Settings to select broadcast bands for any network on each Wi-Fi System node. [NWI-5064]
Refined the deletion procedure and improved backward compatibility when configuring Wi-Fi networks. [NDM-4711]
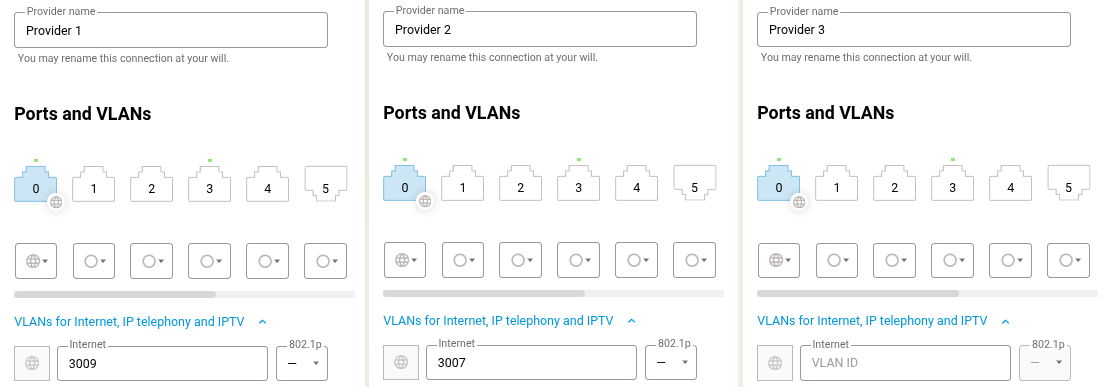
Added support to configure multiple Internet access providers on a single Ethernet port using separate VLANs via Web Interface. [NWI-1279]
Upgraded the libxml2 library to version 2.15.4, resolving the following security issues: CVE-2026-86137, CVE-2026-86138, CVE-2026-86139, CVE-2026-86140, CVE-2026-86141, CVE-2026-86142, CVE-2026-86143, and CVE-2026-86144. [NDM-4676]
Enabled Keyword Filter support in the IntelliQoS application classifier to improve detection efficiency. [NDM-4674]
The following improvements have been applied to the Web Interface.
Multiple blocking rules per client or segment can now be configured when setting up the Keyword Filter. [NWI-5077]
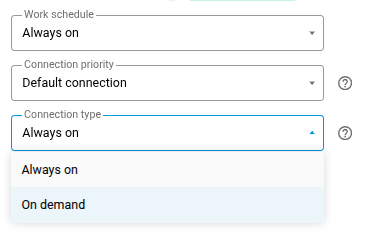
Added an option to select the On demand connection type for Ethernet, DSL and VPN connections to the Internet. [NWI-5072]
Improved the Keenetic Domain Name section with an option to change the registered name for the device. [NWI-5065]
Improved the display of longer texts by implementing line breaks based on syllables. [NWI-5074]
Updated SSL/TLS cipher suite configuration and added ML-KEM support for post-quantum cryptography. [NDM-4663]
The following improvements have been applied to the Web Interface.
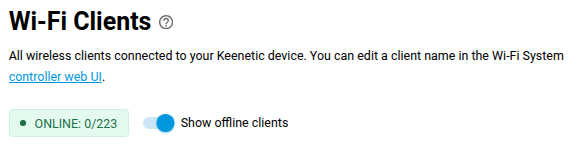
Enhanced the Clients page on Extender devices by adding an option to hide offline clients and a tooltip to display the client count by status. [NWI-5051]
Added a warning when the Registered Clients count reaches its limit. [NWI-713]
The following improvements have been applied to the Web Interface.
Added post-quantum key exchange support with ML-KEM512, ML-KEM768, and ML-KEM1024 via Diffie-Hellman groups 35, 36, and 37 to Site-To-Site IPsec VPN Connections. [NWI-5050]
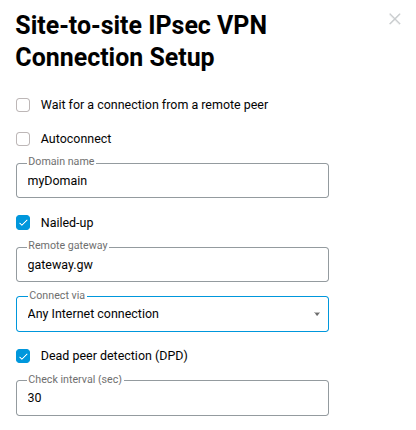
Enabled an option to specify the outbound interface for establishing Site-To-Site IPsec VPN Connections, ensuring correct source IP selection in multi-WAN environments. [NWI-5054]
Upgraded the OpenConnect to version 9.21, addressing multiple issues and enhancements. [NDM-4649]
Enhanced the brute-force lockout policy command set. [NDM-4655]
vpn-server lockout-policy (enable | threshold {thr} | duration {dur} | observation-window {wnd})— set up the lockout policy for the PPTP VPN Server application;ip [http|telnet|ssh] lockout-policy (enable | threshold {thr} | duration {dur} | observation-window {wnd})— set up the lockout policy for device management sessions;show vpn-server lockout-policy— display the lockout details for the PPTP VPN Server application;show ip [http|telnet|ssh] lockout-policy— display the lockout details for device management sessions.
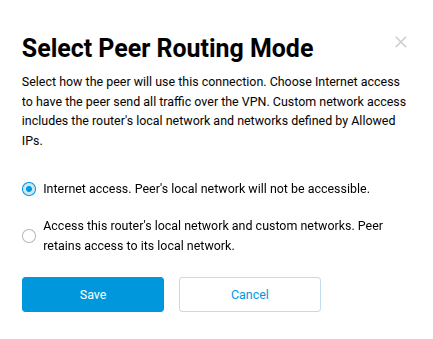
Added the Listen port setting and the client peer routing mode selection to the WireGuard VPN Server application. [NWI-4978]
Upgraded the system authentication method for the HTTP suite to harden security. [NDM-4515]
Enabled post-quantum key exchange for the SSH protocol to comply with modern security standard. [NDM-4299]
The following improvements have been applied to the Web Interface.
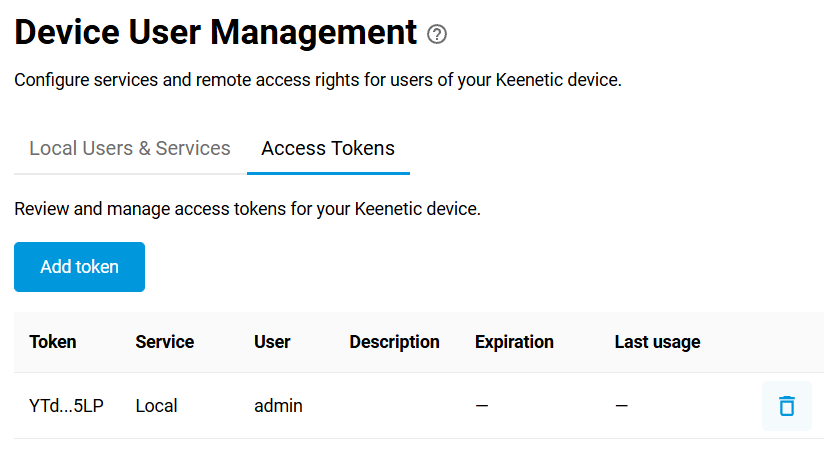
Added access tokens information display on the Users and Access page. [NWI-4923]
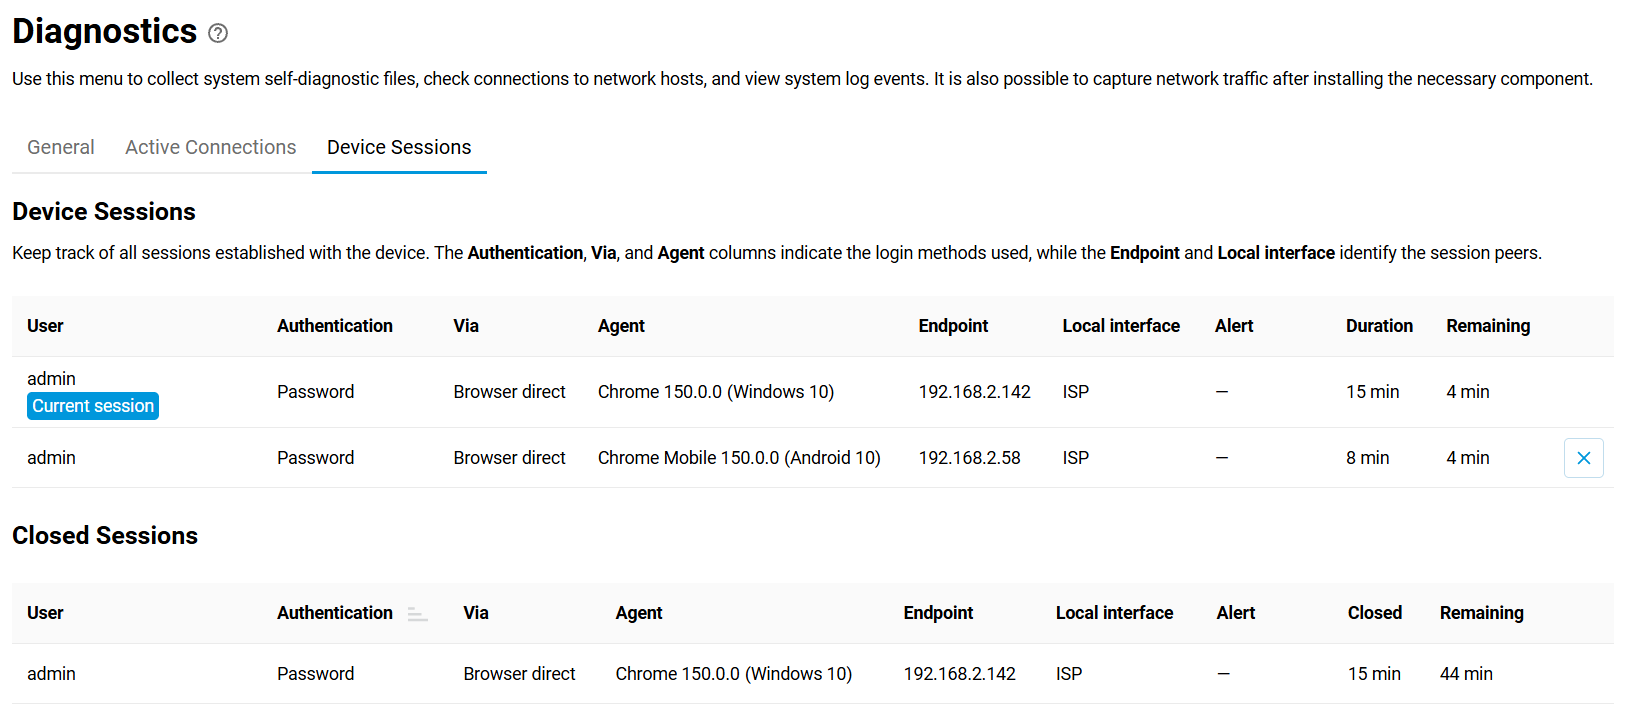
Added a dedicated tab on the Diagnostics page showing system sessions information. [NWI-4924]
Improved the Wireless Access Control page operation when no changes are made to access list. [SYS-1808]
Added support for setting the
host-uniqparameter via the CLI command to maintain compatibility with specific IPv6 connection setups. [NDM-4485]interface {name} pppoe host-uniq {host-uniq}— set the HEX value to thehost-uniqparameter on the{name}PPPoE interface.
Enabled the inclusion of segments without an IP address on the controller node in the Wi-Fi System. [NDM-4443]
Enabled importing OpenVPN connections from a URL via CLI command. [NDM-4556]
interface {name} openvpn import {url}— set up the OpenVPN{name}interface with configuration at{URL}.
Added support for importing WireGuard configurations from a URL via CLI command. [NDM-4555]
interface {name} wireguard import {url} — set up the WireGuard
{name}interface with configuration at{URL}.